

Android · iOS · Web
Information collection from DEX, APK, IPA, Mach-O, HTML, JS, Smali files with directory-level batch scanning; APK/IPA/H5 auto-download and one-shot scanning.
An information-gathering scanner for HW operations / red team / pentest teams — quickly extract URLs, IPs, components, AK/SK and other key assets from Android, iOS, Web/H5, with json / txt / xlsx reporting.
Information collection from DEX, APK, IPA, Mach-O, HTML, JS, Smali files with directory-level batch scanning; APK/IPA/H5 auto-download and one-shot scanning.


AK/SK detection covering Aliyun / Tencent / AWS / Google / GitHub / GitLab / Slack / Stripe / JWT / private keys / URL-embedded passwords and more.


Phone numbers, ID cards, emails, bank cards, license plates, names, passports, VIN, IMEI, USCC and other personal / corporate sensitive data (key items checksum-validated).


20 Android + 22 iOS CVE/RCE component detection; extracts fastjson / bcprov / log4j versions and assesses CVE impact (affected / safe).


Unified 39-vendor packer signature library with three-signal detection; --unpack explicitly unpacks (auto-pushes a version-matched frida-server), --prefer-dump scans existing dumps.


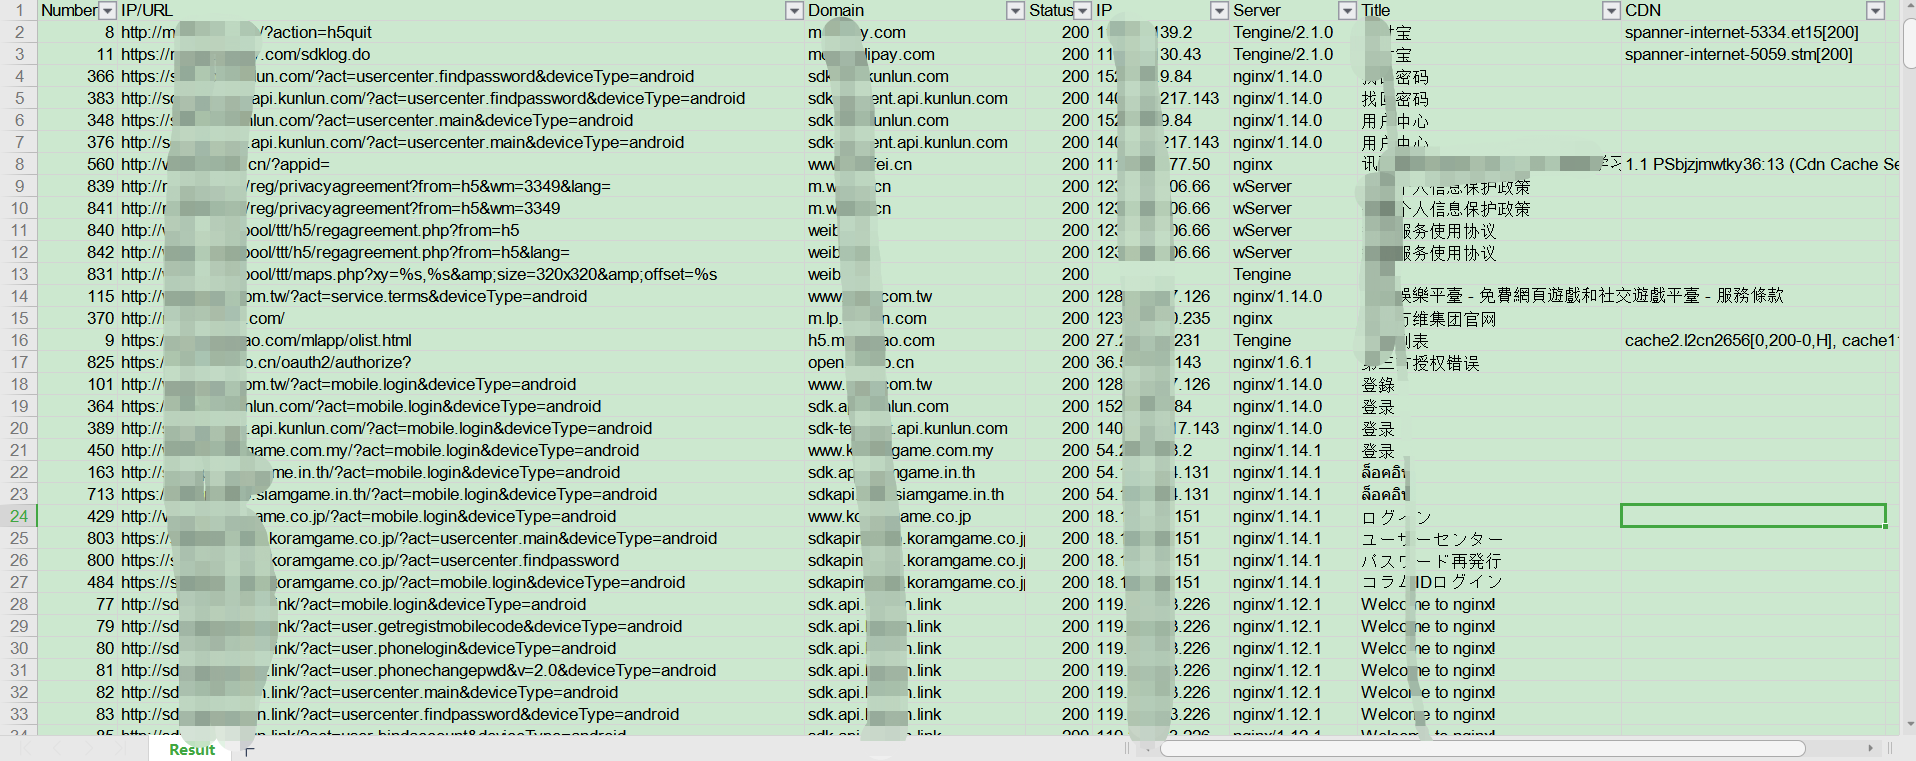
Status code / title / Server / CDN / resolved IP sniffing; --sniffer is explicit opt-in, --scope limits sniffing to an authorized domain list; intranet and loopback are never sniffed.


report.json / report.txt / report.xlsx outputs with sensitive permissions, packer vendors and [!] high-value findings summarized.


The update subcommand checks / downloads / MD5-verifies GitHub Releases; config.toml is versioned with cross-version auto-migration; missing toolchains auto-install on macOS/Linux.
Maintained by an individual developer in spare time (GPL-3.0, 3500+ stars). If it helps you, consider becoming a sponsor, donating, starring the main repo, or contributing a rule to the Rule Center — all equally appreciated.
Disclaimer
Do NOT use this project's techniques or code for malicious software creation, software copyright/IP theft, or improper profit. Violations may constitute violations of the Criminal Law of the People's Republic of China (Articles 217, 286), the Cybersecurity Law, the Computer Software Protection Regulations, and other laws. The techniques mentioned in this project may only be used for private learning and testing in lawful scenarios. The project author is not responsible for any criminal or civil liability arising from improper use of these techniques.